The ICO isn't waiting for a new AI law.
It's enforcing the ones that already exist.
There is no UK AI Act, and the government's deliberately light-touch approach has convinced a great many businesses they have nothing to do. Most are non-compliant and do not know it.
UK GDPR already applies to every AI system that processes personal data. It made no exception for AI and needs no amendment to reach it.
The ICO publishes Guidance on AI and data protection, its own reading of how the law applies to AI. It does not need a new statute to use the powers it already has.
The Equality Act 2010 covers AI in hiring. Where a tool screens or ranks candidates on your behalf, having bought it in is not a defence.
Not sure where you stand? Answer 7 questions and get your free UK AI compliance exposure report — instant, no sign-up.
Take the Free Check →"No UK AI Act" does not mean "no obligation."
The UK Government's AI regulation White Paper took a principles-based, pro-innovation approach — deliberately avoiding prescriptive legislation. Many businesses read this as a green light. It isn't. Existing law already reaches into AI systems in ways most businesses haven't mapped.
UK GDPR applies to every AI system that collects, processes, or makes decisions using personal data about UK individuals. Data minimisation, purpose limitation, fairness, and transparency requirements all apply — and automated decision-making has specific obligations.
The ICO publishes Guidance on AI and data protection, setting out what it expects of businesses using AI. The ICO can and does investigate AI deployments — you don't need to wait for a formal complaint. Pro-active audits of high-risk AI uses are part of the ICO's published enforcement strategy.
The Equality Act 2010 applies to AI systems used in recruitment, promotion, disciplinary proceedings, or any employment decision. If your AI tool produces outputs that indirectly discriminate on protected characteristics — even unintentionally — you have liability.
The FCA has published AI guidance and expects firms to apply existing regulatory obligations — fairness, explainability, governance — to AI systems. FCA-regulated firms using AI in credit decisions, customer communications, or risk assessment have obligations beyond UK GDPR.
The ICO issued its first AI-specific enforcement action in 2024. Businesses can no longer claim ignorance of how existing law applies to their AI tools.
United Kingdom
There is no UK AI Act. That is the sentence that gets businesses into trouble.
“Britain hasn’t passed an AI law, so there is nothing for us to do yet.”
True — and beside the point. Here is what already applies to you.
-
UK GDPR
Applies to every AI system that collects or processes personal data about UK individuals. Data minimisation, purpose limitation, fairness and transparency all apply, and automated decision-making carries its own obligations.
-
The ICO’s Guidance on AI and data protection
Published, and the regulator’s own reading of how the law applies to AI. Proactive audits of high-risk AI use are part of the ICO’s stated strategy — you do not need a complaint against you first.
-
Employment law
The Equality Act 2010 does not care whether a decision was made by a person or a model. AI used in hiring, performance or disciplinary decisions is judged on its outcomes.
-
Your regulator, if you have one
The FCA expects firms to apply existing obligations — fairness, explainability, governance — to AI. Financial services using AI in credit, communications or risk assessment have duties beyond UK GDPR.
Waiting for a UK AI Act is not a compliance position. The laws that already exist are the ones being enforced.
UK AI regulation: different from the EU, but not absent.
The UK's retained version of GDPR applies to all AI systems that process personal data. Automated decision-making provisions, transparency requirements, and data subject rights obligations all apply to AI deployments. This is the primary compliance obligation for most UK businesses using AI.
The ICO's guidance covers accountability and governance, transparency, lawfulness, accuracy, fairness, security and data minimisation, and individual rights in AI systems. Businesses without documented AI governance are exposed.
Any AI system used in employment decisions must not produce outputs that discriminate — directly or indirectly — on protected characteristics. This isn't a new obligation. It's the Equality Act applied to AI. Most HR AI tools have never been assessed against it.
The government's AI Regulation White Paper established five principles: safety, security, transparency, fairness, accountability, and contestability. These are currently non-statutory guidance applied by sector regulators. Future legislation may codify them. Building your framework around these principles now ensures resilience as the landscape firms up.
28 dates that decide whether you are compliant.
14 of them have already passed.
United Kingdom is one line of 9. The businesses we see are rarely on only one. Yours is marked. The others reach you through your customers, your staff and your suppliers, wherever you are registered.
Europe
- in force Obligations for general-purpose AI models.
- in force Article 50 transparency duties and enforcement powers for national regulators.
- coming New prohibitions, and Article 50(2) marking of synthetic content.
- coming Every Member State must have an AI regulatory sandbox running.
- coming High-risk obligations for Annex III systems — including AI used in recruitment, credit scoring, education and essential services.
- coming High-risk obligations for Annex I systems — AI embedded in products already covered by EU product safety law.
United Kingdom this page
- in force Most Part 5 data protection provisions of the Data (Use and Access) Act 2025, including the wider lawful bases for solely automated decisions and the safeguards that come with them.
- in force The duty on controllers to operate a complaints procedure and respond to data protection complaints within set time limits.
United States
- in force New York City Local Law 144 — an employer or agency using an automated employment decision tool for a New York City job needs a bias audit within the past year, published results, and notice to candidates.
- in force Washington My Health My Data Act (RCW 19.373) — consent before collecting or sharing consumer health data and a published health data privacy policy, for any business targeting Washington consumers; small businesses from 30 June 2024. A breach is an unfair practice under the Consumer Protection Act.
- in force Utah Artificial Intelligence Policy Act (SB 149, 2024) — a business using generative AI with a consumer must say so when the consumer clearly asks; licensed professions must disclose it up front in high-risk interactions. Narrowed by SB 226 from 7 May 2025, with a safe harbour for disclosing at the start.
- in force Texas HB 149, the Responsible Artificial Intelligence Governance Act — prohibited uses, government AI disclosure, and Attorney General enforcement.
- in force California SB 942, the AI Transparency Act — free AI detection tool and latent provenance disclosure for large generative AI providers. Delayed from 1 January 2026 by AB 853.
- coming Colorado SB 26-189 — developer and deployer duties for automated decision-making technology used in consequential decisions. It repealed and reenacted SB 24-205, which never took effect. California SB 1050 (Chapter 246, Statutes of 2026) — an advert shown in California that prominently features an AI-generated performer who looks or sounds human must say so clearly, in words like "this performance features a synthetic performer". Any size of business; enforced as false advertising. California CCPA regulations on automated decisionmaking technology (Cal. Code Regs. tit. 11, s. 7200) — a business using ADMT for a significant decision about a consumer must give pre-use notice, opt-out and access rights. In force 1 January 2026; businesses already using ADMT must comply by this date. Only businesses within the CCPA. Connecticut Public Act 26-15, sections 4 to 6 — duties on operators of AI companions, including detecting and responding to signs of self-harm. Washington HB 2225 (Chapter 168, Laws of 2026) — AI companion chatbots must disclose that they are not human, with safeguards for minors and a private right of action. A customer-service bot that does not sustain a relationship is excluded. Oregon SB 1546 (Chapter 85, Oregon Laws 2026) — operators of AI companions must tell users they are not talking to a person, keep a protocol for users who express thoughts of suicide or self-harm, and add safeguards for minors; a user who is harmed can sue. Software used solely for customer service, business operations or productivity is excluded.
- coming Idaho Conversational AI Safety Act (S 1297, Session Law Chapter 249 of 2026; Idaho Code Title 48, Chapter 21) — a conversational AI service open to the public must say it is AI where a person could be misled, answer prompts about suicide with a crisis referral, and protect account holders who are minors. Enforced by the Attorney General. A chatbot used only for customer service or a business's own operations is excluded.
- coming Connecticut Public Act 26-15 (Substitute SB 5, 2026), sections 7 to 12 — any business doing business in Connecticut that uses an automated employment-related decision technology for a hiring, promotion or discipline decision must disclose it and give written notice before the decision. No size threshold. A breach is an unfair trade practice.
- coming California CCPA regulations, s. 7157 — risk assessments conducted in 2026 and 2027 must be submitted to the California Privacy Protection Agency by this date.
Canada
- in force Ontario ESA / O. Reg. 476/24 — a publicly advertised job posting must disclose the use of AI to screen, assess or select applicants. Employers of 25 or more, including where a third party screens on their behalf.
Australia
- coming Privacy Act 1988 (Cth), APP 1.7 — a privacy policy must say what kinds of personal information a computer program uses to make decisions that could reasonably be expected to significantly affect a person, and what kinds of decisions those are — the automated decision-making (ADM) transparency obligations, regulated by the OAIC.
United Arab Emirates
- in force DIFC Data Protection Regulation 10 — a business deploying an autonomous or semi-autonomous system that processes personal data must tell users, on first use, what the system decides for itself, what it was built to do and what it does with the output.
Saudi Arabia
- in force The Saudi Data and AI Authority's grace period under the Personal Data Protection Law ends, and with it the undertaking not to apply penalties. The authority has said it may extend the grace period for a business that gives it good reason.
South Korea
- in force Framework Act on the Development of Artificial Intelligence and Establishment of a Foundation for Trust in force. A business in the AI industry must tell users in advance where a product runs on generative or high-impact AI, and label what generative AI produces. It applies to conduct outside Korea that affects the Korean market or its users.
China
- in force Personal Information Protection Law in force. A business outside China that handles the personal information of people in China — to offer them products or services, or to analyse their behaviour — must have a lawful basis for it and must appoint a representative or a dedicated body inside the country. Nothing in the duty turns on how much data is held.
If any of these apply to your business, you have compliance obligations today.
- Using any AI tool that processes personal data about UK individuals (UK GDPR applies)
- AI-assisted CV screening, candidate ranking, or any hiring or HR decisions
- Automated decisions about customers that have meaningful effects (pricing, credit, access)
- FCA-regulated firms using AI in customer communications, risk modelling, or credit decisions
- Healthcare, legal, or education organisations deploying AI in service delivery
- Any UK business that wants a documented, defensible AI governance position
Read it before you buy it.
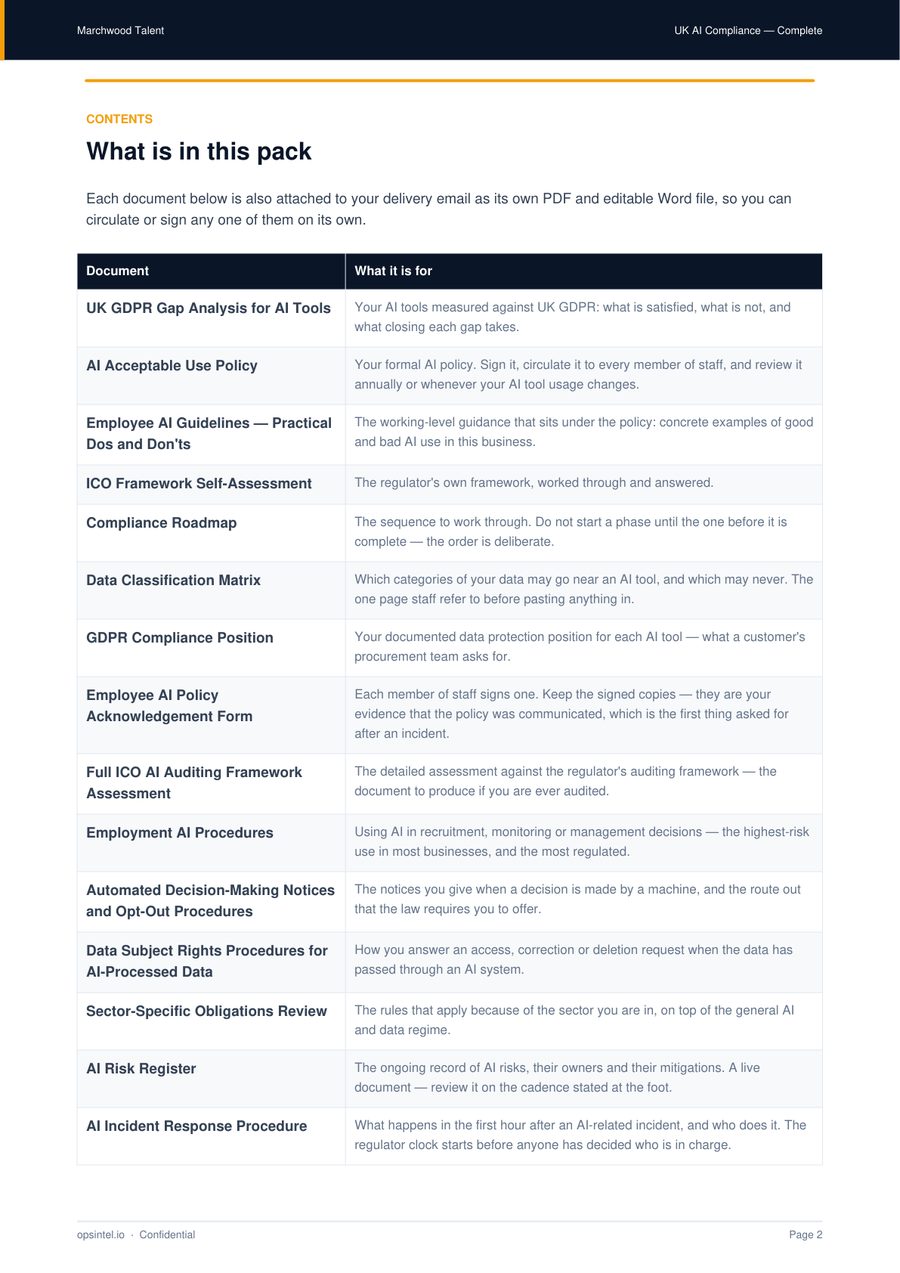
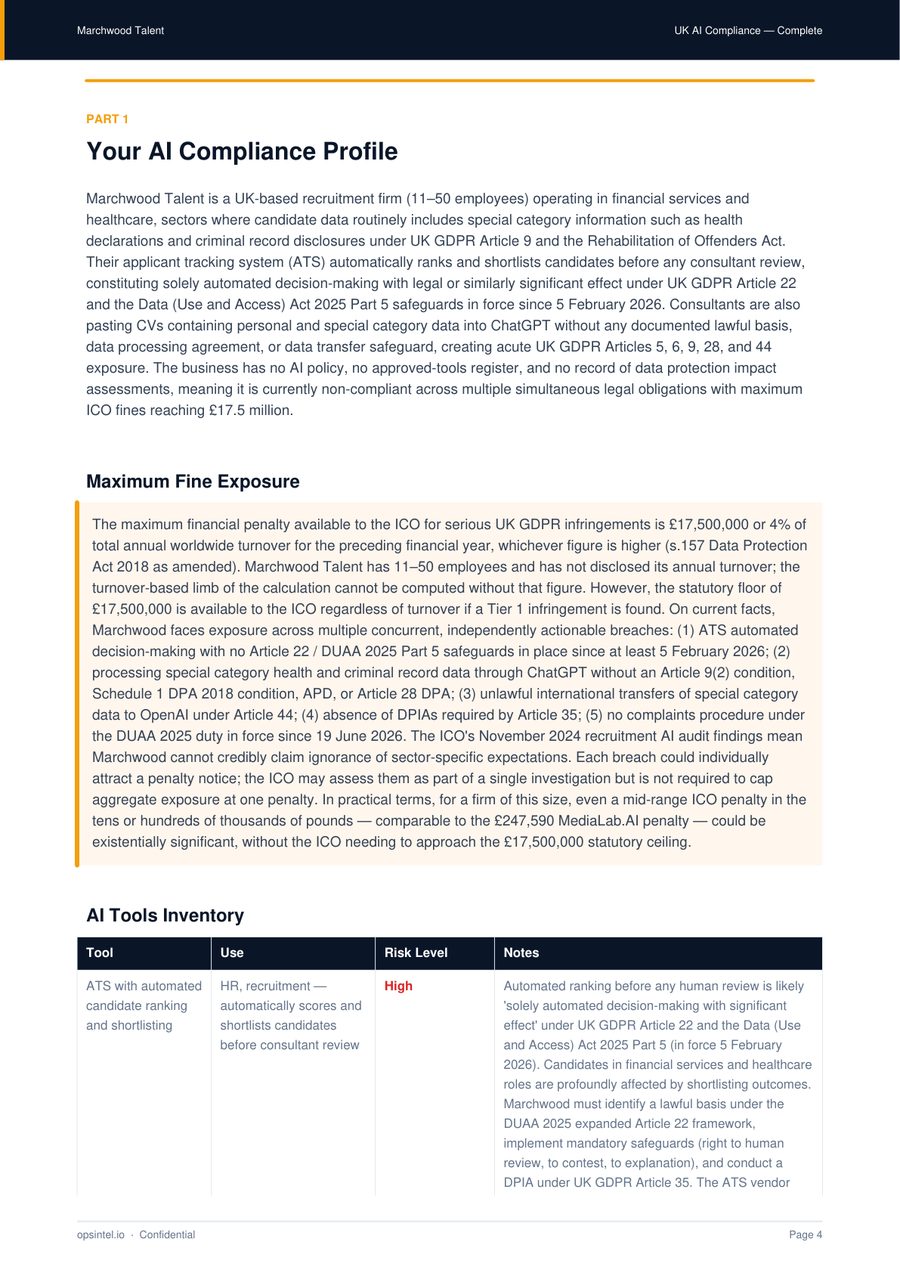
This is not a mock-up or a contents page. It is a genuine UK AI Compliance pack — all 20 documents — produced by the same system that will produce yours, for a fictional recruitment firm we invented to test it. Their AI shortlists candidates, so the pack is written around that. Yours is written around whatever your business does.
26 September 2026 — added: Answers to the AI questions clients send their suppliers
The gap. Public bodies and large companies now send their suppliers questions about the AI they use. Our frameworks held most of the answers, but a client had to know where to look, usually with a renewal waiting.
What we added. The questions real buyers publish, each put in plain words, with the document in your framework that answers it and anything still yours to do.
24 September 2026 — added: ISO/IEC 42001 and NIST AI RMF alignment map
The gap. Bigger clients, insurers and tenders can ask a supplier whether its AI governance meets ISO/IEC 42001 or the NIST AI Risk Management Framework. Our frameworks held most of the evidence, but nothing in them showed it.
What we added. A map that names, clause by clause, which of your documents meets each standard and what is still yours to do. It shows alignment, not certification.
Every framework, in all seven markets, has these changes. The pages below were made before them, so they show 2 documents fewer than a framework bought today.
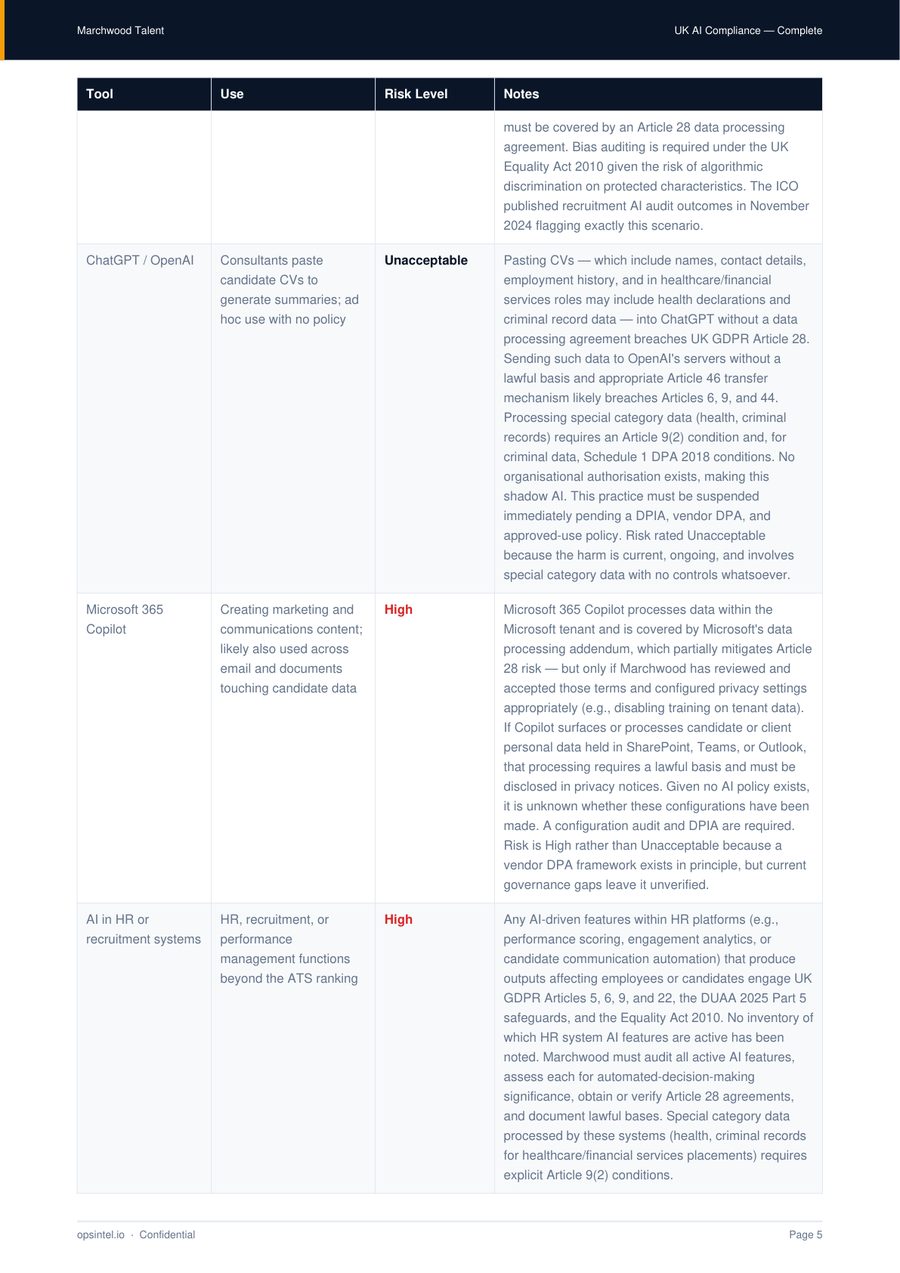
This framework also comes with a compliance dashboard you run all year: a dated to-do list, your AI tools and their risks, staff sign-off, an incident log, every document to download, the deadlines for your markets and a statement you can share. See a fictional example → · What the dashboard does →
Build to what the ICO already audits, not to a statute that may never arrive.
Waiting for a UK AI Act assumes the duties start when it does. They do not, and the shape of them is already published. The government's five principles — safety, security, transparency, fairness, accountability and contestability — are non-statutory guidance that sector regulators apply today, and the ICO's audit framework asks its own questions of the same systems. Neither is a forecast. Both are what an investigation opens with.
So the durable move is to build to the principles, not to a bill. Do that and you hold a documented position now — and if Parliament codifies those principles, it tests a framework you already have rather than one you are writing under deadline. That is what the annual renewal is for: when the ICO, a sector regulator or Parliament moves, your framework moves with it, and you are not paying to start again.
Not sure which of these already bind you? Seven questions, no sign-up.
Take the free check →
Your customers decide which law
applies to you. Not your address.
Where your customers are, where your staff are and where your AI has effect — those decide, not where the business is registered. We write frameworks to four legal systems, and serve four more on request.
- United Kingdom UK GDPR, in force now. The Data (Use and Access) Act added automated-decision duties from 5 February 2026.
- European Union The EU AI Act. General-purpose AI obligations already apply; regulators have had enforcement powers since 2 August 2026.
- United States State by state, not federal. Texas from 1 January 2026, California from 2 August 2026, Colorado from 1 January 2027.
- Canada PIPEDA plus provincial law. Ontario's AI hiring disclosure rules applied from 1 January 2026.
UK AI Compliance Packages.
Every package builds a documented, defensible compliance position for your business. Prices in GBP. Stripe accepts all major cards.
- UK GDPR gap analysis for your AI tools
- AI Acceptable Use Policy (UK-specific)
- Employee AI guidelines
- Self-assessment against the ICO’s AI guidance
- Basic compliance roadmap
- ISO/IEC 42001 and NIST AI RMF alignment map
Best for: small businesses wanting to understand and document their UK GDPR obligations for the AI tools they're already using.
In your inbox by the end of the business day · Covers you for 12 months, renews yearly
Buy now — £797/year →- Everything in UK AI Compliance Foundation
- Full assessment against the ICO’s AI guidance
- Employment AI procedures (Equality Act compliance)
- Automated decision-making notices and opt-out procedures
- Data subject rights procedures for AI-processed data
- Sector-specific obligations review (finance, health, legal)
- ISO/IEC 42001 and NIST AI RMF alignment map
- Your AI compliance dashboard: a to-do list, your AI tools, staff sign-off, an incident log, every document and a shareable statement
Best for: businesses using AI in HR or employment decisions, FCA-regulated firms, or any business wanting a comprehensive, ICO-ready compliance position.
In your inbox by the end of the business day · Covers you for 12 months, renews yearly
Renews yearly — ICO guidance and legislation updates applied throughout your cover.
Buy now — £1,297/year → or book a scoping call firstEvery framework is annual — your fee covers 12 months of protection, with ICO guidance updates and UK AI regulation developments applied to your framework as they land, and renews yearly so your cover never lapses.
The same work, done in-house.
718 pages of primary law to read, 14 documents to write, and 15 records a year to keep afterwards. Costed against what a member of staff on the median UK salary actually costs an hour:
£4,586
Your own staff — 177 hours of their time
£797/year
UK AI Compliance — in your inbox by the end of the business day
Bought, built and delivered without a meeting.
Buy it
Buy it on this page. There is no call to book and no slot to wait for. If you would rather talk it through first, that option is there too.
Tell us about you
A dozen questions: your sector, your size, where you operate, the AI tools you use, what those tools decide, and what you are worried about.
It arrives
Your framework is written from your answers against UK GDPR, the ICO's Guidance on AI and data protection and the employment rules that apply to you — in your inbox by the end of the business day. PDF and Word, the full pack and every document on its own.
It stays current
For 12 months we watch ICO guidance and UK AI regulation. When something moves, we confirm it against the regulator’s own source, rebuild your documents and email them to you. Renews yearly.
Straight answers.
Is UK AI compliance different from EU AI Act compliance?
Yes, significantly. The EU AI Act is prescriptive legislation with specific requirements by risk category — it's a detailed rulebook. The UK government deliberately chose a different path: a principles-based approach applied through existing sector regulators rather than a single AI-specific law. In practice, UK compliance is less about ticking boxes on a new law and more about demonstrating that your existing obligations under UK GDPR, employment law, and sector regulations extend to your AI systems — and that you've documented your governance accordingly.
What does the ICO expect from a business using AI?
The ICO's Guidance on AI and data protection is organised around seven areas: accountability and governance (who is responsible for AI decisions?), transparency (can individuals understand how AI affects them?), lawfulness (is there a lawful basis for the processing?), accuracy (are AI outputs accurate and regularly tested?), fairness (are AI outputs fair and non-discriminatory?), security and data minimisation (is the data secured, and only what is necessary?), and individual rights (can people exercise their rights over AI-processed data?). Businesses with documented AI governance across these areas are in a substantially better position than those without.
Does the Equality Act apply to off-the-shelf AI tools I didn't build?
Yes. The Equality Act 2010 applies to the employer's actions, not the tool's source code. If you use an AI tool in a hiring or employment decision and the outputs are discriminatory — even if the tool was supplied by a third party — you carry the liability. Indirectly discriminatory outputs (for example, a CV screening tool that systematically deprioritises certain names or universities) can trigger Equality Act exposure.
We're a small business. Does this really apply to us?
UK GDPR applies to all businesses that process personal data, regardless of size — there are no small-business exemptions for AI systems. That said, proportionality matters: the ICO expects your compliance to be proportionate to your size and the risks involved. Our Starter package is specifically designed for small businesses that need a proportionate, practical compliance position without enterprise-level complexity.
Is this legal advice?
No. We produce compliance documentation frameworks and policy documents — we are not solicitors. For businesses in regulated sectors or facing specific ICO investigations, we recommend reviewing your documentation with UK-qualified legal counsel. For most businesses using standard AI tools, our frameworks provide a practical, well-documented compliance position that demonstrates good-faith effort to the ICO.
Get your UK AI compliance framework in place.
The ICO is already investigating AI deployments. UK GDPR already applies to your AI tools. The Equality Act already covers AI in employment decisions. Build your compliance position now.
See the Packages →Or book a free 20-minute call to discuss your situation — hello@opsintel.io