AI compliance isn't just a policy document.
It's a system.
A policy tells your team what to do. A compliance framework makes sure they actually do it — and gives you evidence if anyone ever asks.
Tick what your business actually does.
apply to you
Nothing selected — tick one above and watch.
Not sure which package you need? Answer 7 questions and get your free AI compliance exposure report — instant, no sign-up.
Take the Free Check →UK, EU, and US AI compliance — choose the jurisdiction you need.
Choose the framework that matches where your customers, employees, and operations are. Need more than one? We offer bundles — or you can start with one and extend later.
For businesses operating in the UK. Covers UK GDPR, ICO obligations, SRA/FCA sector requirements, and AI acceptable use. Starter from £797.
For any business with EU customers, employees, or operations. Banned-practice and GPAI rules already in force; high-risk obligations land December 2027. Applies to UK and US businesses. Essentials from €597.
For businesses with US operations, employees, or customers. California, Texas and Illinois laws are live now. Policy from $247.
UK Compliance Frameworks
- Acceptable Use Policy
- Data Classification Matrix
- GDPR Compliance Position (up to 5 AI tools)
- Employee Guidelines + Acknowledgement Forms
- ISO/IEC 42001 and NIST AI RMF alignment map
- Answers to the AI questions clients send their suppliers
- A private log-in to your framework: every document to download, and any dates still ahead in the laws it covers
When a client, insurer or tender asks how your firm uses AI, you have a written answer ready to send.
In your inbox by the end of the business day · Covers you for 12 months
If anything in our documents turns out to be wrong in law, tell us and we fix it within two business days, for as long as your cover runs.
Renews yearly — legal updates applied throughout your cover as regulation evolves.
Buy now — £797/year → or book a scoping call first- Everything in Foundation Framework
- AI Risk Register (populated for your current tools)
- Incident Response Procedure
- Staff briefing session (60 min, remote)
- Annual reassessment at renewal included
- ISO/IEC 42001 and NIST AI RMF alignment map
In your inbox by the end of the business day · Covers you for 12 months
If anything in our documents turns out to be wrong in law, tell us and we fix it within two business days, for as long as your cover runs.
Renews yearly — legal updates applied throughout your cover as regulation evolves.
Best for: regulated businesses (FCA, SRA, ICO), businesses with 10+ employees, any business handling significant client data.
Buy now — £1,297/year → or book a scoping call first- Your fee covers a full 12 months — then renews yearly
- Legal updates applied as UK AI regulation evolves
- Quarterly review of tools, policies, and regulatory changes
- Unlimited tool additions and policy changes covered
- Priority response if you receive an ICO enquiry or data subject request
No separate retainer, no surprise invoices — one annual fee keeps you covered and current.
Questions? Book a call →EU AI Act Compliance
Prohibited-practice and general-purpose AI rules are already in force; high-risk obligations land 2 December 2027. Applies to any business with EU customers, employees, or operations — not just EU companies. UK businesses with Irish clients, US businesses with German users — all in scope.
- EU AI Act risk tier classification for all AI tools in use
- Gap analysis against Annex III high-risk obligations
- Article 50 transparency requirements assessment
- Documented EU compliance position
- Supply chain risk review
In your inbox by the end of the business day
Best for: businesses already actively trading with EU clients who need standalone EU compliance.
Buy now — £1,500 → or book a scoping call first- All 14 steps on the EU AI Act route, each with a document of its own
- Everything in Full Compliance Framework (UK)
- EU AI Act risk classification + Annex III gap analysis
- Article 50 transparency obligations
- Cross-border data governance documentation
- Supply chain compliance review
- Staff briefing covering both UK and EU obligations
- Saves £400 versus purchasing separately
- ISO/IEC 42001 and NIST AI RMF alignment map
- Your AI compliance dashboard: a to-do list, your AI tools, staff sign-off, an incident log, every document and a shareable statement
In your inbox by the end of the business day · Covers you for 12 months, renews yearly
If anything in our documents turns out to be wrong in law, tell us and we fix it within two business days, for as long as your cover runs.
Best for: any business operating across UK and EU markets — the most comprehensive option available.
Buy now — £2,400/year → or book a scoping call first- For existing Ops Intel UK Full Compliance clients only
- Upgrades your existing framework to cover EU AI Act
- No duplication of work already completed
- EU risk classification + Article 50 compliance
- Updated documentation covering both jurisdictions
In your inbox by the end of the business day
Best for: existing clients expanding into EU trading. Contact us to confirm eligibility.
Enquire — £900 →US AI Compliance
California, Texas and Illinois AI laws are live now. Illinois law applies to any employer using AI in hiring decisions — regardless of which state your business is in.
- AI Acceptable Use Policy
- Employee AI guidelines
- AI tool inventory template
- Plain-English summary of obligations by state
Best for: small businesses wanting a baseline policy covering all 50 states.
In your inbox by the end of the business day
Buy now — $247 →- Everything in US AI Policy
- State obligations assessment (CA, CO, TX, IL)
- Employment AI disclosure notices
- Algorithmic discrimination prevention procedures
- Consumer-facing AI transparency disclosures
- ISO/IEC 42001 and NIST AI RMF alignment map
- Answers to the AI questions clients send their suppliers
- A private log-in to your framework: every document to download, and any dates still ahead in the laws it covers
When a client, insurer or tender asks how your firm uses AI, you have a written answer ready to send.
In your inbox by the end of the business day
If anything in our documents turns out to be wrong in law, tell us and we fix it within two business days, for as long as your cover runs.
Buy now — $997/year → or book a scoping call first- Everything in Foundation
- Multi-state compliance matrix
- Full HR AI procedures and disclosure templates
- Impact assessment templates
- Incident response procedure
- Federal legislation readiness assessment
- ISO/IEC 42001 and NIST AI RMF alignment map
Best for: multi-state businesses, 15+ employees, or businesses wanting full coverage ahead of federal legislation.
In your inbox by the end of the business day · Covers you for 12 months, renews yearly
If anything in our documents turns out to be wrong in law, tell us and we fix it within two business days, for as long as your cover runs.
Buy now — $1,897/year → or book a scoping call firstEvery framework is annual — your fee covers 12 months of protection, new state AI laws monitored and applied to your framework as they pass, and renews yearly so your cover never lapses.
The detail, when you want it.
Why a policy alone is not enough
Pick your market. Buy today.
Fixed price. Plain English. Written for how your business actually uses AI.
Australia and New Zealand
Australasia AI Compliance — Foundation
A$1,597/year
Buy now → What's includedNot sure which laws reach you? Take the free two-minute check and it will tell you, or ask us on WhatsApp.
Most businesses stop at the policy. The framework is what actually protects you.
- A document
- States the rules
- Given to employees once
- Sits in a folder
- No evidence of compliance
- A system
- Enforces the rules
- Regularly reviewed and updated
- Evidenced and auditable
- Demonstrates due diligence to ICO, regulators, and clients
The six parts of a framework
A complete AI compliance framework has six components.
Acceptable Use Policy
The foundation document. Defines approved tools, prohibited uses, data rules, and employee responsibilities. Customised to your business.
Data Classification Matrix
Categorises every type of data your business handles (public, internal, confidential, restricted) and defines which AI tools each category can be processed by.
GDPR Compliance Position
For each AI tool you use: is it a data processor? Is there a DPA? Where is data stored? Does it train on your inputs? Documented and maintained.
Employee Guidelines & Acknowledgement
Plain-English guidelines per team and role. Employees read, understand, and sign acknowledgement. You have a record.
AI Risk Register
A live document listing every AI tool in use, the risks associated with each, and the mitigations in place. Updated when tools are added or changed.
Incident Response Procedure
What happens if something goes wrong. Who is notified, in what order, within what timeframe. Required by UK GDPR for data incidents.
Regulated industries
Regulated industries have additional obligations.
Legal (SRA regulated)
Client confidentiality, legal professional privilege, and SRA Code of Conduct obligations apply when using AI with client matter files. The SRA has published specific guidance.
Financial Services (FCA regulated)
The FCA expects firms to manage AI as an operational risk. Consumer Duty obligations extend to AI-assisted advice or communications.
Healthcare & Care
CQC and ICO requirements overlap. Special category health data has the highest level of GDPR protection. Any AI processing of patient or service user data requires explicit justification.
Education
If children's data is involved, additional safeguarding obligations apply. Ofsted may ask about AI use in safeguarding contexts.
Trading with Europe: the EU AI Act
Trading with Europe? The EU AI Act already applies to you.
The EU AI Act is not just a European regulation. It has explicit extraterritorial reach — if your AI systems produce outputs used inside the EU, you are in scope. That includes any UK business with Irish clients, EU supply chain partners, or EU-based customers.
Prohibited AI practices banned
Manipulative AI, social scoring, and mass biometric surveillance outlawed across the EU — including outputs from UK-based systems reaching EU users.
Fines now enforceable
EU regulators can issue fines today. Up to €35 million or 7% of global annual turnover, whichever is LOWER for a small or medium business — in practice 7% of turnover for serious violations. No grace period on prohibited practices.
Enforcement powers live
Article 50 transparency obligations apply and national regulators across all EU member states have their enforcement powers. This is the milestone that affects most businesses.
High-risk AI systems (Annex III)
Recruitment, credit scoring, education and essential-services AI come into scope. Deferred from August 2026 by the Digital Omnibus, adopted 29 June 2026.
AI in regulated products
AI embedded in medical devices, vehicles, and regulated machinery faces its own compliance deadline.
Who This Catches
UK businesses with any customers in Ireland or mainland Europe
B2B suppliers whose end clients serve EU customers
Businesses processing data about EU citizens
Any business planning EU expansion — build it now, not later
See a sample framework
Read it before you buy it.
This is not a mock-up or a contents page. It is a genuine UK + EU Combined Compliance Framework — all 32 documents — produced by the same system that will produce yours, for a fictional firm of solicitors we invented to test it. Every page below came out of the real thing.
14 October 2026 — added: AI literacy under the EU AI Act: your measures and the record of them
The gap. The EU AI Act asks every business that uses AI to take measures so the people using it for them understand it. Our UK + EU framework had staff guidelines and a briefing, but nothing that set out those measures group by group or recorded that they were taken.
What we added. A record, from the Act as amended by the Digital Omnibus, of what each group of people using AI for you needs to understand, contractors included, with room for the measure you take, how you show it and when it was done.
14 October 2026 — added: A register of every AI tool you use, with its EU role and risk
The gap. Every duty in the EU AI Act attaches to a particular tool. Our UK + EU framework tested each tool and classified its risk, but had no single list of the tools themselves.
What we added. One register, a row per tool, showing what it is for, who supplies it, the data it touches, whether it is AI under the Act, your role with it, its risk tier and who owns it.
14 October 2026 — added: Your duties as a user of AI under the EU AI Act, as a checklist
The gap. The EU AI Act gives a business that uses AI duties of its own, separate from the duties of whoever makes the tool. Our UK + EU framework had no single list of them.
What we added. Every duty the Act gives a user of AI, from Articles 4, 26, 27, 50 and 86, saying which apply to every business and which only to a high-risk tool, with room to record how each is met.
14 October 2026 — added: A fundamental rights impact assessment: whether you need one, and the record if you do
The gap. The EU AI Act asks some users of high-risk AI to assess its effect on people's rights before first use. Our UK + EU framework did not show who that applies to or what the assessment must hold.
What we added. Questions that show whether Article 27 asks you for the assessment, then every element it must contain, with the Digital Omnibus change that lets it cross-refer to your data protection impact assessment.
14 October 2026 — added: A record of the data going into each AI tool
The gap. A user of a high-risk AI tool must make sure the data it puts in is fit for the tool's purpose. Our UK + EU framework covered data protection, but not this.
What we added. A row per tool for the data you put in, whether it is relevant and representative, the data protection impact assessment, and who may put data in, with the Digital Omnibus rules on sensitive data used to correct bias.
14 October 2026 — added: Monitoring, logs and when to stop using an AI tool
The gap. A user of a high-risk AI tool must watch how it runs, keep its logs, and stop and report when it presents a risk. Our UK + EU framework had an incident procedure, but no record of the monitoring itself.
What we added. A row per tool for what to watch, who checks and how often, where its logs are kept and for how long, and the last check, with when the Act says to stop using a tool and whom to tell.
Every framework bought today has these changes. The pages below were made before them, so they show 6 documents fewer than a framework bought today.
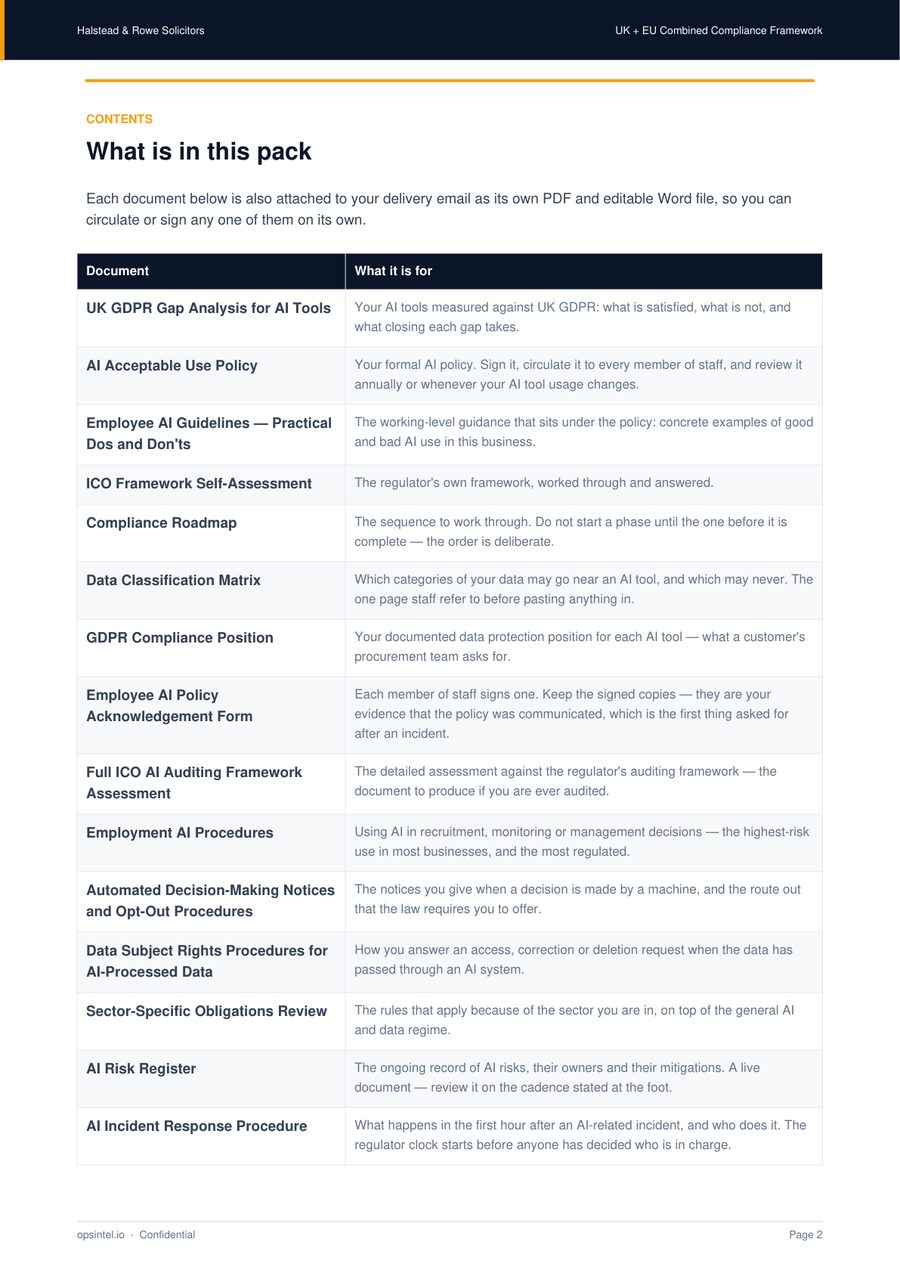
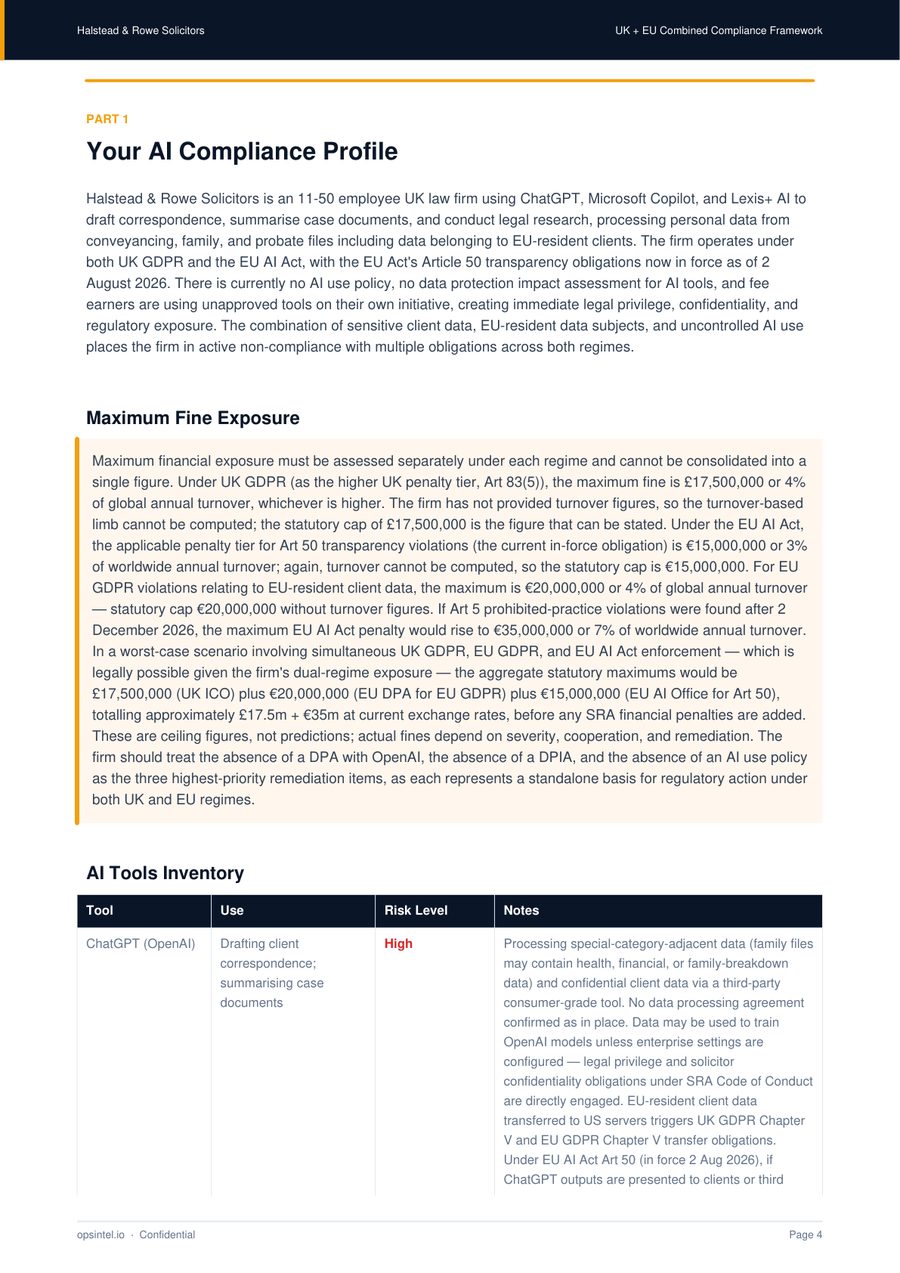
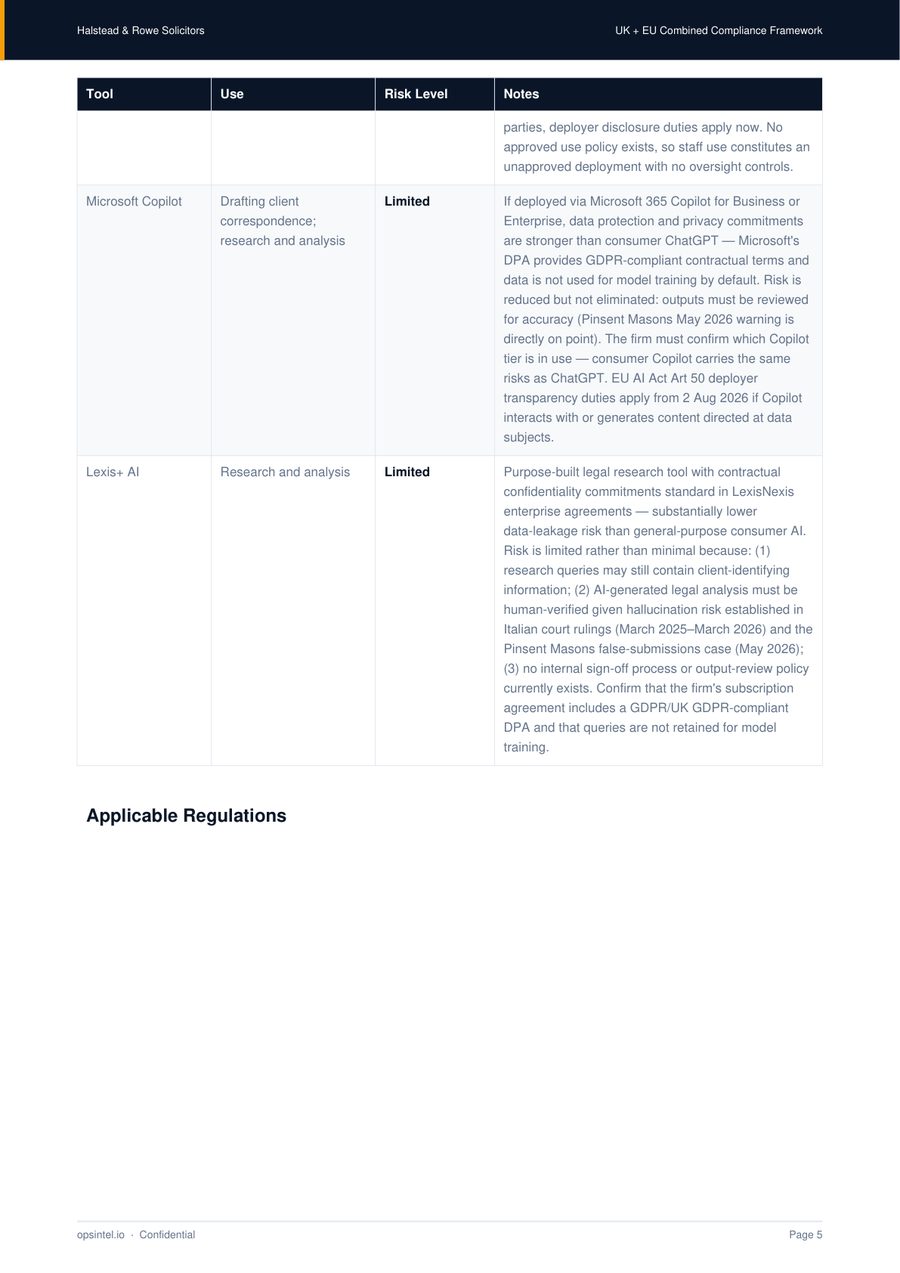
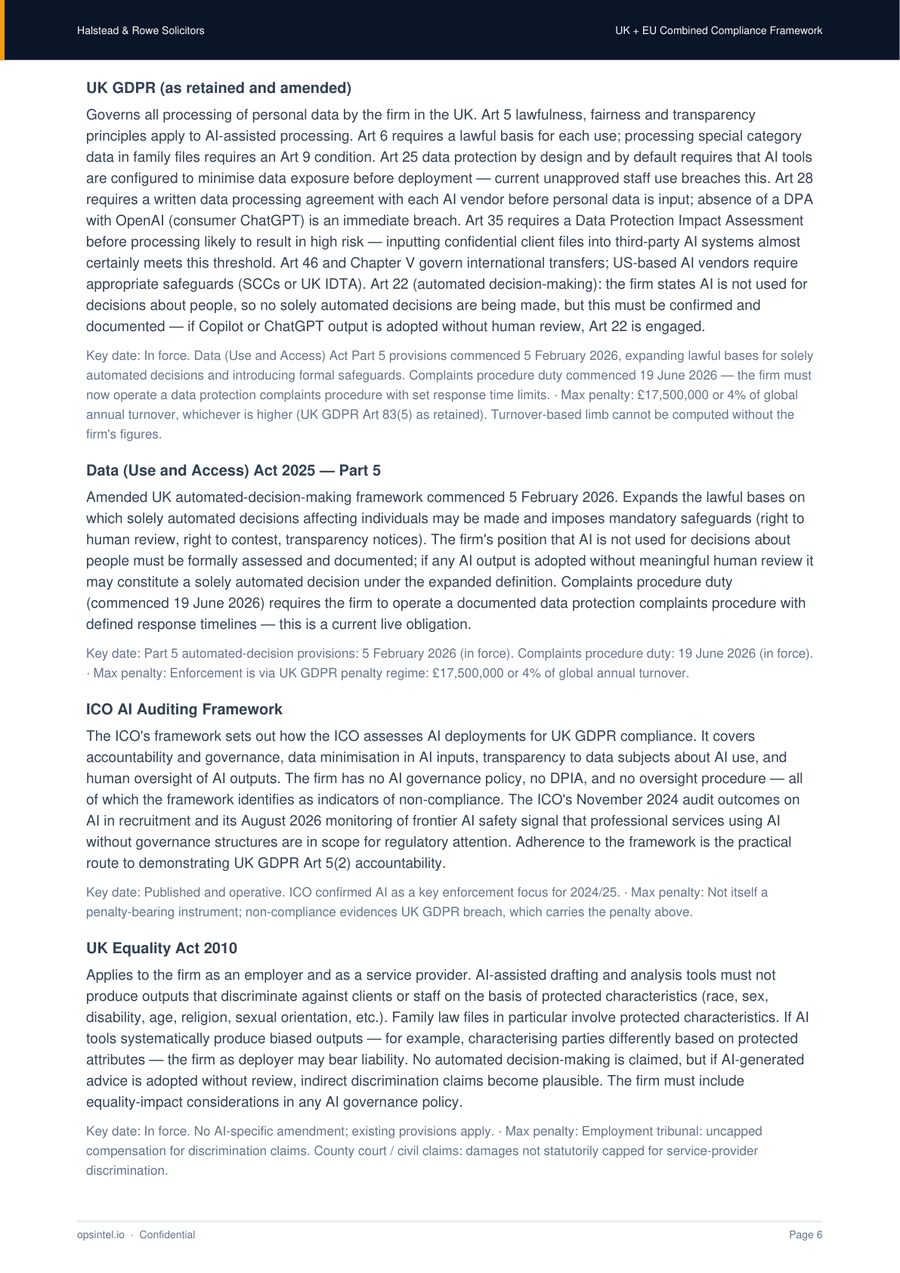
This framework also comes with a compliance dashboard you run all year: a dated to-do list, your AI tools and their risks, staff sign-off, an incident log, every document to download, the deadlines for your markets and a statement you can share. See a fictional example → · What the dashboard does →
Why not a £15,000 assurance engagement
You don't need a £15,000 "AI Assurance" engagement. You need a compliance framework that actually works.
Larger consultancies are now selling "AI Governance" and "AI Assurance" programmes — broad, expensive, and built for enterprises with months to spare. Most SMEs need something different: clear documentation, practical policies, and a defensible compliance position, delivered fast.
Large AI Assurance Firms
- ✗ 6–12 week discovery process before any deliverable
- ✗ Scoping fees, daily rates, change requests — total cost unknown upfront
- ✗ Frameworks built for enterprise scale, not a 10-person professional services firm
- ✗ You still need to operationalise it yourself afterwards
Ops Intel
- ✓ Fixed price — you know the full cost before you commit
- ✓ Complete framework delivered in days, not months
- ✓ Built specifically for SMEs in professional services — not scaled down from enterprise
- ✓ Includes staff briefing, acknowledgement forms, and legal updates throughout your 12-month cover
For most SMEs, the question isn't whether to get compliant — it's whether to do it affordably now, or expensively later.
What it costs to do it yourself
The same work, done in-house.
862 pages of primary law to read, 38 documents to write, and 15 records a year to keep afterwards. Costed against what a member of staff on the median UK salary actually costs an hour:
£9,627
Your own staff — 371 hours of their time
£2,400/year
UK + EU Combined Compliance Framework — in your inbox by the end of the business day
How it works, from buying to delivery
Bought, built and delivered without a meeting.
-
01
Buy it
Buy it on this page. There is no call to book and no slot to wait for. If you would rather talk it through first, that option is there too.
-
02
Tell us about you
A dozen questions: your sector, your size, where you operate, the AI tools you use, what those tools decide, and what you are worried about.
-
03
It arrives
Every document is written from your answers and emailed to you — in your inbox by the end of the business day. That includes your team’s part: plain-English staff guidance, a training syllabus, and an acknowledgement form for them to sign and file.
-
04
It stays current
For 12 months we watch the law where you operate. When something moves, we confirm it at the source, rebuild your documents and email them to you. Renews yearly.
Sample reports
See exactly what you receive.
Every framework is tailored to your business, your AI tools, and your jurisdictions. These samples show the range — from a clean low-risk result through to a business with significant gaps to close.
Example A — Low Risk
Harrison & Cole Accountants Ltd
Prepared by Ops Intel · Jurisdictions: United Kingdom · European Union
Executive Summary
ShownHarrison & Cole is a 14-person chartered accountancy practice in Leeds. The firm uses AI tools across email drafting, transaction categorisation, tax return preparation, and receipt processing.
All AI systems are limited-risk or minimal-risk under the EU AI Act. Primary exposure: transparency obligations under Article 50 and sub-processor controls for financial data.
AI System Inventory
ShownEvery AI tool the firm uses is catalogued — purpose, data involved, and whether it's client-facing.
| ID | System | Provider | Purpose | Client-facing? |
|---|---|---|---|---|
| AI-001 | Microsoft 365 Copilot | Microsoft | Email drafting, document summarisation, client correspondence | Indirectly |
| AI-002 | Xero (AI features) | Xero Ltd | Transaction categorisation, smart reconciliation | No |
| AI-003 | QuickBooks AI | Intuit | Expense categorisation, bookkeeping suggestions | No |
| AI-004 | IRIS Elements AI | IRIS Software | Tax return data extraction | No |
| AI-005 | Dext | Dext Ltd | OCR receipt and invoice extraction | No |
| AI-006 | ChatGPT (ad hoc) | OpenAI | Ad hoc drafting — no policy in place | No policy |
EU AI Act — Risk Classification
ShownEach AI system is classified under the EU AI Act four-tier risk framework. Risk tier determines which obligations apply.
No prohibited or high-risk AI systems in use.
Risk Register
Client ConfidentialAI Usage Policy
Client ConfidentialGap Analysis & Remediation Roadmap
ShownEvery gap is assigned a priority, a target date, and a clear action. Nothing is left as "review required."
EU AI Act Art. 50 · DUA Act 2025 Target: 31 July 2026
DUA Act 2025 · UK GDPR · ICO guidance Target: 30 June 2026
UK GDPR · EU AI Act Target: 31 May 2026
Target: 31 July – 30 September 2026
Data Governance · Vendor Management · Incident Response · Training · Sign-off
Client ConfidentialYour framework. Your AI tools. Your regulations.
In your inbox by the end of the business day. Accurate as at delivery, then kept current — your framework renews annually with legal updates included.
Sample report. Client name, trading details, and AI tool configuration are illustrative only. Any resemblance to actual organisations is coincidental.
Example B — High Risk
Apex Creative Agency Ltd
Prepared by Ops Intel on behalf of Apex Creative Agency Ltd · Jurisdictions: United Kingdom · European Union · United States
Executive Summary
ShownApex Creative Agency Ltd is a 22-person digital marketing agency based in Manchester, delivering paid media, content, and creative services to clients across the UK, EU, and North America. The agency uses AI tools extensively across campaign delivery, copywriting, image generation, client reporting, and outreach.
AI System Inventory
Shown7 AI systems identified across campaign delivery, content production, client outreach, and reporting.
| ID | System | Provider | Purpose | DPA in place? | Client data? |
|---|---|---|---|---|---|
| AI-001 | ChatGPT (consumer) | OpenAI | Ad copy, emails, client briefs, proposals | ✗ No | Yes — uncontrolled |
| AI-002 | Midjourney | Midjourney Inc. | Client creative assets, social imagery, ad visuals | ✗ No | Client brand assets |
| AI-003 | Meta Advantage+ | Meta Platforms | Automated audience targeting and creative optimisation | ~ Partial | Client audience data |
| AI-004 | Google Performance Max | Google LLC | Automated campaign management and targeting | ~ Partial | Client audience data |
| AI-005 | HubSpot (AI features) | HubSpot Inc. | CRM email drafting, lead scoring, contact enrichment | ✓ Yes | Prospect data |
| AI-006 | Jasper AI | Jasper AI Inc. | Long-form content, blog posts, landing page copy for clients | ✗ No | Client briefs, brand guides |
| AI-007 | Whatagraph (AI reports) | Whatagraph Ltd | Automated client performance reporting | ✓ Yes | Client campaign data |
EU AI Act — Risk Classification
ShownThree systems carry active transparency obligations under Article 50. Two require immediate deployer review under Article 26.
Risk Register
Client ConfidentialAI Usage Policy
Client ConfidentialGap Analysis & Remediation Roadmap
Shown9 gaps identified. 6 are high priority. The roadmap sequences remediation to address the highest legal exposure first.
UK GDPR Art. 28 · Art. 32 · DUA Act 2025 Target: Immediate — restrict use today
EU AI Act Art. 50(4) — synthetic content disclosure Target: Before next campaign launch
UK GDPR Art. 28 — processor agreement required Target: 31 May 2026
EU AI Act Art. 50(1) & Art. 50(4) Target: 30 June 2026
EU AI Act Art. 26 — deployer obligations Target: 31 July 2026
DUA Act 2025 · UK GDPR · ICO AI guidance Target: 30 June 2026
Target: 31 July – 30 September 2026
Data Governance · Vendor Management · Incident Response · Training · Sign-off
Client ConfidentialIf this looks familiar, the time to act is now.
EU AI Act transparency obligations apply from August 2026. In your inbox by the end of the business day. Your framework renews annually with legal updates included, so it keeps pace as the rules change.
Sample report. Client name, trading details, and AI tool configuration are illustrative only. Any resemblance to actual organisations is coincidental.
Quick answers.
Do we need a framework or just a policy?
Depends on size and sector. For a 2-person business using ChatGPT occasionally: a policy is probably enough. For a solicitors' firm with 8 staff using multiple AI tools with client data every day: the full framework is appropriate. Our free AI risk checker tells you which side of that line you are on in about a minute.
Can this be used if the ICO investigates us?
Yes. One purpose of the framework is to demonstrate due diligence. If the ICO investigates a data incident, having documented policies, training records, and a risk register is material evidence of responsible data handling.
How often does it need updating?
The AI landscape changes fast. We recommend reviewing your policy and risk register every 12 months minimum, or whenever you adopt a significant new AI tool. Your framework renews annually with legal updates included, so the regulatory side is handled for you — just tell us when you adopt a new tool.
We're UK-only right now — do we need EU coverage?
If you have no clients, suppliers, or data subjects in EU member states (including Ireland), the UK framework is sufficient for now. However, if there's any chance you'll expand into EU markets in the next 12–24 months, building EU compliance in from the start is significantly cheaper than retrofitting it later. The EU Extension at £900 is available to existing UK Full Compliance clients when you're ready to make that move.
Does the EU AI Act really apply to a small UK business?
Yes — if your AI systems produce outputs used inside the EU. The Act's extraterritorial scope is explicit. A UK solicitor with one Irish client using AI to assist with their work is in scope. A UK marketing agency with one EU-based client is in scope. The fines are proportional for SMEs, but proportional is not zero — and the reputational risk of an enforcement action is the same regardless of company size.
Is this legal advice?
No. Our compliance frameworks are general compliance guidance documents and do not constitute legal advice. Ops Intel is not a law firm and is not authorised by the Solicitors Regulation Authority or Financial Conduct Authority. We recommend seeking independent legal advice for specific regulatory questions relating to your circumstances. Our frameworks are designed to demonstrate due diligence and reasonable steps — the standard most regulators apply when assessing SME compliance.
Don't wait for an incident to get compliant.
Book a 30-minute call. We'll assess what your business actually needs and give you a clear quote.
Book a Free Compliance Call →Free 30-minute call · Written quote before work starts · In your inbox by the end of the business day · UK-based team
Pick your market. Buy today.
Fixed price. Plain English. Written for how your business actually uses AI.
Australia and New Zealand
Australasia AI Compliance — Foundation
A$1,597/year
Buy now → What's includedNot sure which laws reach you? Take the free two-minute check and it will tell you, or ask us on WhatsApp.