Dubai already has binding AI rules. Most firms working there have never read them.
The Gulf is usually described as having no AI law. For the Dubai International Financial Centre that is simply wrong, and has been for years: Regulation 10 of the DIFC Data Protection Regulations governs personal data processed through autonomous and semi-autonomous systems, and it binds.
What makes it bite for ordinary firms is who it names. The duty falls on the deployer — the business operating the system or getting the benefit of it — whether or not that business built the tool, hosts it, or controls what it does. Buying software off the shelf does not move the obligation to the vendor.
Across the wider UAE there is no single AI statute. Personal data is governed federally, and Abu Dhabi Global Market and the DIFC each run their own regime, so where you are registered decides which rules you are under.
Qatar and Saudi Arabia both bind AI through their data laws rather than through an AI law, and both are routinely described as stricter than they are. Qatar was the first in the Gulf to pass a personal data statute at all. Its central bank does impose hard AI rules, including approval before a high-risk system goes live — on the banks and insurers it licenses, and on nobody else. Saudi Arabia has no binding AI statute at all: what governs an AI deployment there is the data law, the transfer rules and your sector regulator's controls.
What actually governs AI in United Arab Emirates, Dubai International Financial Centre, Qatar and Saudi Arabia.
No summaries of summaries. Each of these was read at the publisher's own site, and the obligation is stated as the thing you have to do rather than the clause it comes from.
United Arab Emirates
Federal Decree-Law No. 45 of 2021 on the Protection of Personal Data. There is no federal AI statute.
Handle personal data lawfully across the whole business, and know which of the country's regimes you sit under — the federal law, the DIFC or ADGM — because they are not the same and registration decides it. The federal law reaches a controller or processor outside the UAE that handles the personal data of people inside it, so being registered elsewhere does not put you outside it. A company in a free zone that has its own personal data law is outside it, and under that instead. The federal law does not require a business to appoint a representative or agent in the UAE.
Dubai International Financial Centre
DIFC Data Protection Regulation 10, on personal data processed through autonomous and semi-autonomous systems.
Tell people, on first use, that they are dealing with a system that acts on its own — what it was built to do, where it is allowed to decide things for itself, what it produces and what you do with the output. High-risk uses need an Autonomous Systems Officer and certification under the Commissioner's framework. Neither the DIFC Data Protection Law nor its Regulations require a representative inside the DIFC.
Qatar
The Personal Data Privacy Protection Law, Law No. 13 of 2016 — the first of its kind in the Gulf. There is no AI statute. The Law covers personal data processed electronically, and it does not say whether a business outside Qatar is covered.
Process personal data lawfully and fairly, tell people what you are doing with it, keep it secure, and answer their requests. The Law does not require a business to appoint a representative or agent in Qatar. Data of a special nature — about health, physical or psychological condition, children, ethnic origin, religious belief, marriage or criminal offences — may only be processed with permission from the department the Law names. If you are licensed by the Qatar Central Bank, its Artificial Intelligence Guideline binds you on top of this, and a high-risk system needs the regulator's approval — the contract for it included — before it goes live.
Saudi Arabia
The Personal Data Protection Law. There is no binding AI statute.
Have a lawful basis for the personal data your AI uses, meet the transfer rules when that data leaves the Kingdom, and hold the security controls your sector's regulator sets. What binds an AI system here comes from the data law and from sector rules, not from an AI law. It reaches you even if you have no presence in Saudi Arabia: the law covers anyone outside the Kingdom processing the personal data of people inside it, and the authority is directed to enforce it beyond the border. Neither the Law nor its Implementing Regulation requires a business outside the Kingdom to appoint a representative there.
The Saudi Data and AI Authority publishes AI Ethics Principles and guidance on generative AI. Neither is law and neither carries a penalty — but alignment with them is increasingly asked for in public-sector procurement.
17 dates that decide whether you are compliant.
11 of them have already passed.
United Arab Emirates is one line of 9. Yours is marked. The DIFC was binding while most of Europe was still consulting. If you also have customers or staff elsewhere, you are on more than one of these.
Europe
- in force Obligations for general-purpose AI models.
- in force Article 50 transparency duties and enforcement powers for national regulators.
- coming New prohibitions, and Article 50(2) marking of synthetic content.
- coming Every Member State must have an AI regulatory sandbox running.
- coming High-risk obligations for Annex III systems — including AI used in recruitment, credit scoring, education and essential services.
- coming High-risk obligations for Annex I systems — AI embedded in products already covered by EU product safety law.
United Kingdom
- in force Most Part 5 data protection provisions of the Data (Use and Access) Act 2025, including the wider lawful bases for solely automated decisions and the safeguards that come with them.
- in force The duty on controllers to operate a complaints procedure and respond to data protection complaints within set time limits.
United States
- in force Texas HB 149, the Responsible Artificial Intelligence Governance Act — prohibited uses, government AI disclosure, and Attorney General enforcement.
- in force California SB 942, the AI Transparency Act — free AI detection tool and latent provenance disclosure for large generative AI providers. Delayed from 1 January 2026 by AB 853.
- coming Colorado SB 26-189 — developer and deployer duties for automated decision-making technology used in consequential decisions. It repealed and reenacted SB 24-205, which never took effect.
Canada
- in force Ontario ESA / O. Reg. 476/24 — a publicly advertised job posting must disclose the use of AI to screen, assess or select applicants. Employers of 25 or more, including where a third party screens on their behalf.
Australia
- coming Privacy Act 1988 (Cth), APP 1.7 — a privacy policy must say what kinds of personal information a computer program uses to make decisions that could reasonably be expected to significantly affect a person, and what kinds of decisions those are.
United Arab Emirates this page
- in force DIFC Data Protection Regulation 10 — a business deploying an autonomous or semi-autonomous system that processes personal data must tell users, on first use, what the system decides for itself, what it was built to do and what it does with the output.
Saudi Arabia
- in force The Saudi Data and AI Authority's grace period under the Personal Data Protection Law ends, and with it the undertaking not to apply penalties. The authority has said it may extend the grace period for a business that gives it good reason.
South Korea
- in force Framework Act on the Development of Artificial Intelligence and Establishment of a Foundation for Trust in force. A business in the AI industry must tell users in advance where a product runs on generative or high-impact AI, and label what generative AI produces. It applies to conduct outside Korea that affects the Korean market or its users.
China
- in force Personal Information Protection Law in force. A business outside China that handles the personal information of people in China — to offer them products or services, or to analyse their behaviour — must have a lawful basis for it and must appoint a representative or a dedicated body inside the country. Nothing in the duty turns on how much data is held.
Does this apply to you?
Most firms read a page like this and conclude it is about somebody bigger. These are the things that decide it, and the first one catches almost everybody.
- You are registered in the DIFC and run anything that answers customers, screens applicants or scores risk.
- You bought the system in. Regulation 10 names the deployer, not just the developer.
- Your customer-facing notices describe your data handling but say nothing about what the system decides on its own.
What we would do about it.
We build AI compliance frameworks — the policy, the register of where AI touches your business, the record that shows a regulator you thought about it before something went wrong. Fixed price, plain English, written for a business owner rather than a lawyer.
Every price, every line and every figure below is read from the same place the checkout reads it, so what the page says and what you are charged cannot drift apart.
- Which countries in the region reach your business, and on what basis
- AI Acceptable Use Policy
- Employee AI guidelines
- Data processing documentation for AI tools
- Cross-border data transfer position
- Basic compliance roadmap
In your inbox by the end of the business day · annual — covers you for 12 months, renews yearly, legal updates included
Buy Foundation — £797/year →- Everything in Middle East AI Compliance Foundation
- Local representative requirements assessment
- Consumer-facing AI transparency disclosures
- AI Risk Register (populated for your current tools)
- Incident Response Procedure
- HR AI procedures and disclosure templates
In your inbox by the end of the business day · annual — covers you for 12 months, renews yearly, legal updates included
Buy Complete — £1,497/year →Not sure which countries reach you? That is the first document in both tiers, and it names the ones that do not as well as the ones that do. If you would rather talk it through first, the call below is free and there is no pitch deck.
Read it before you buy it.
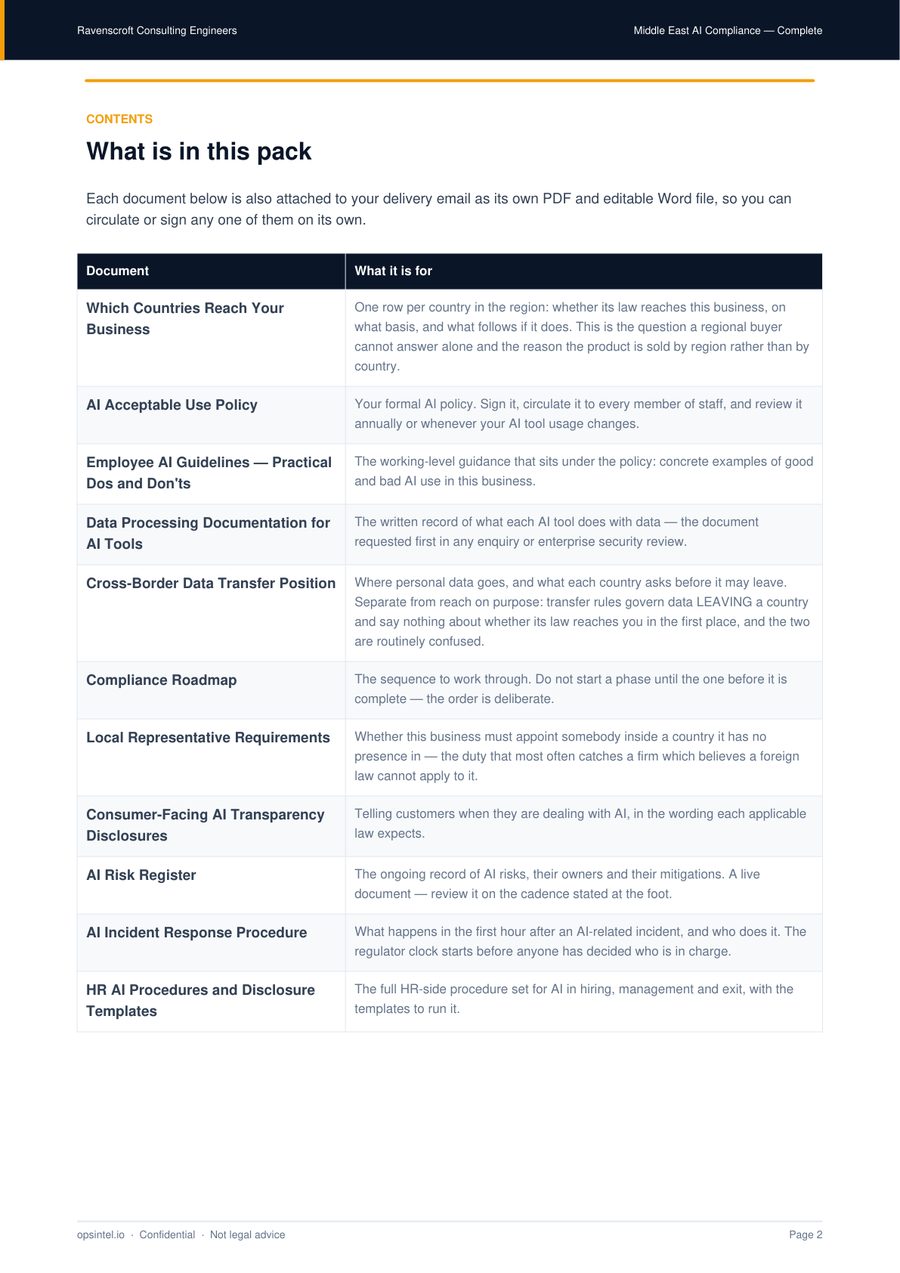
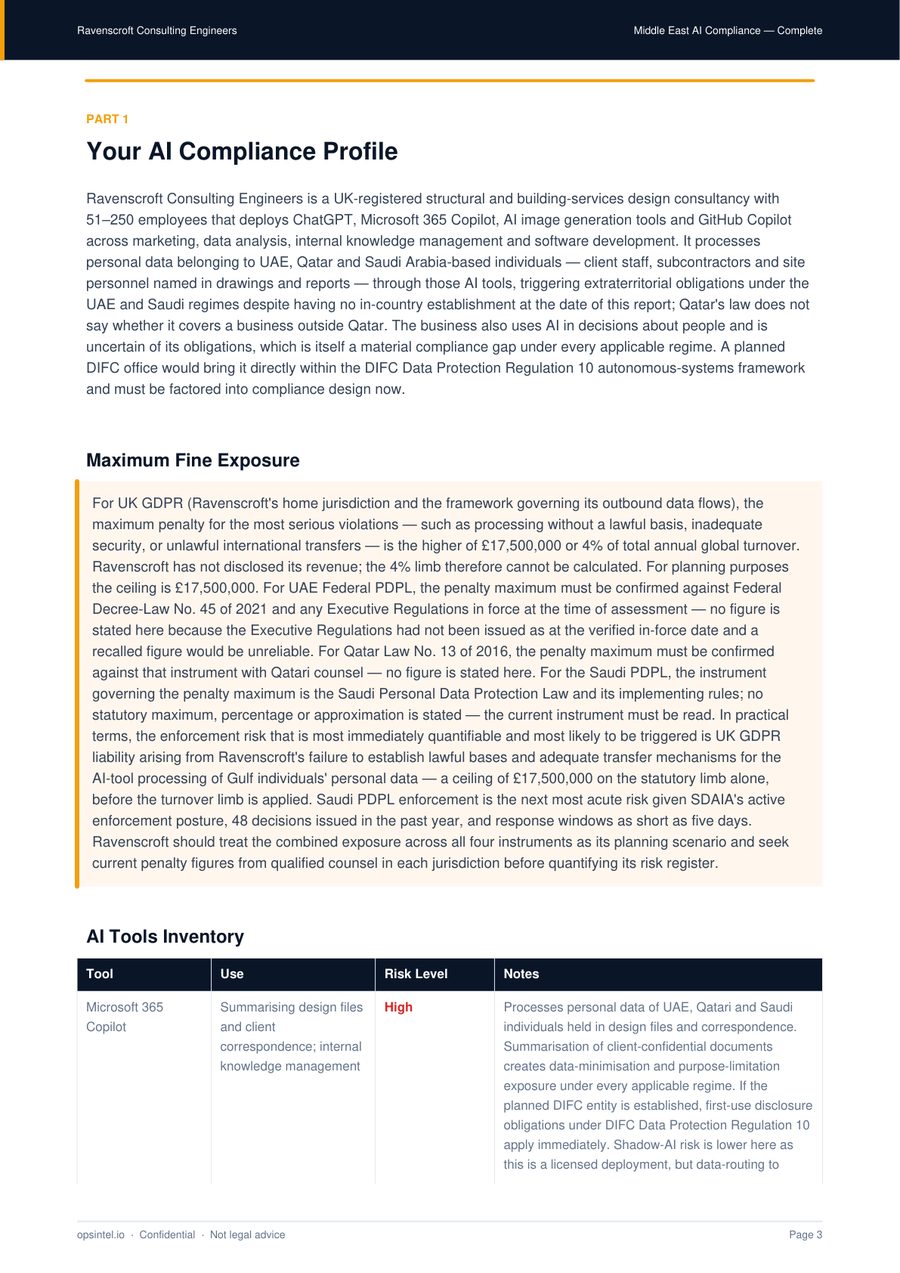
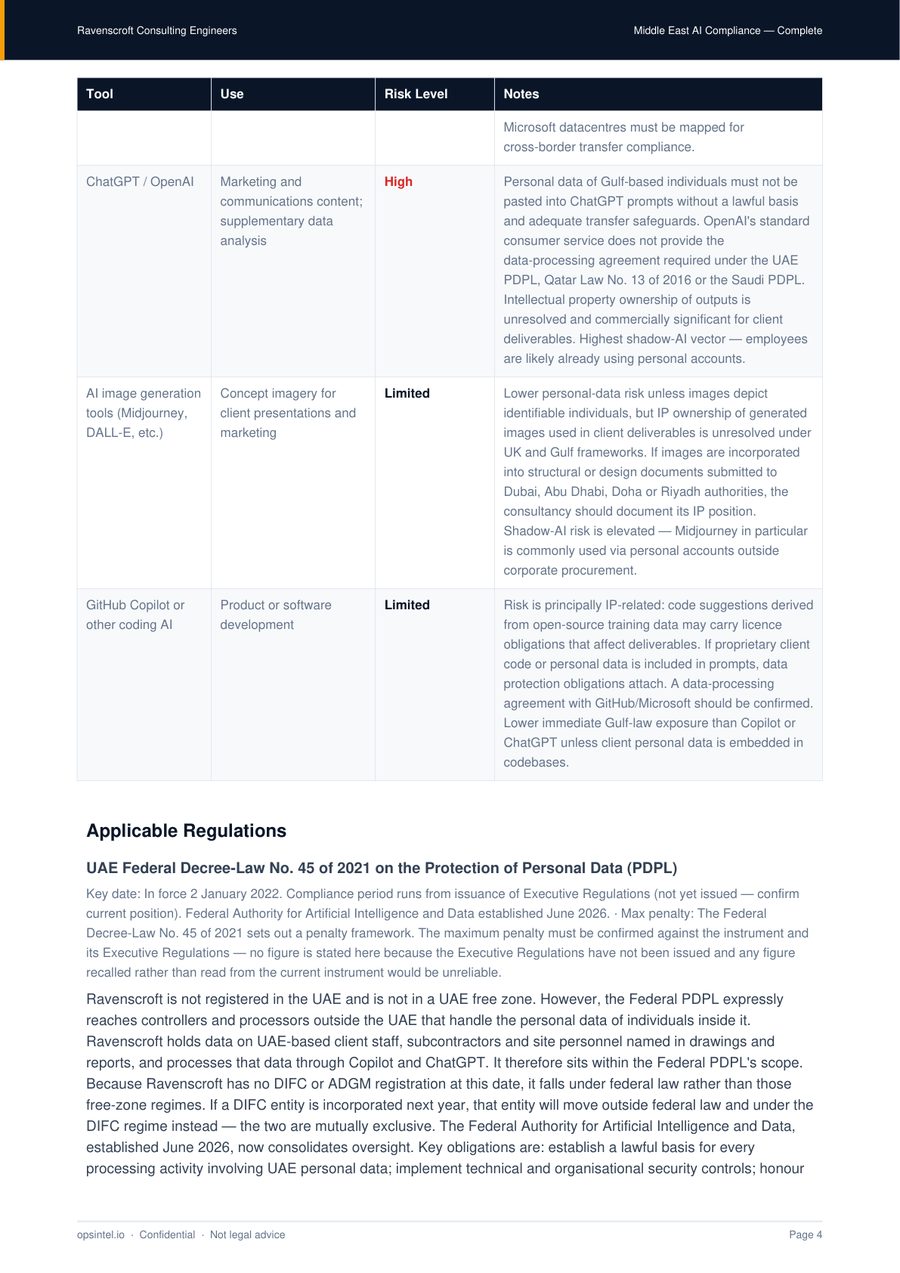
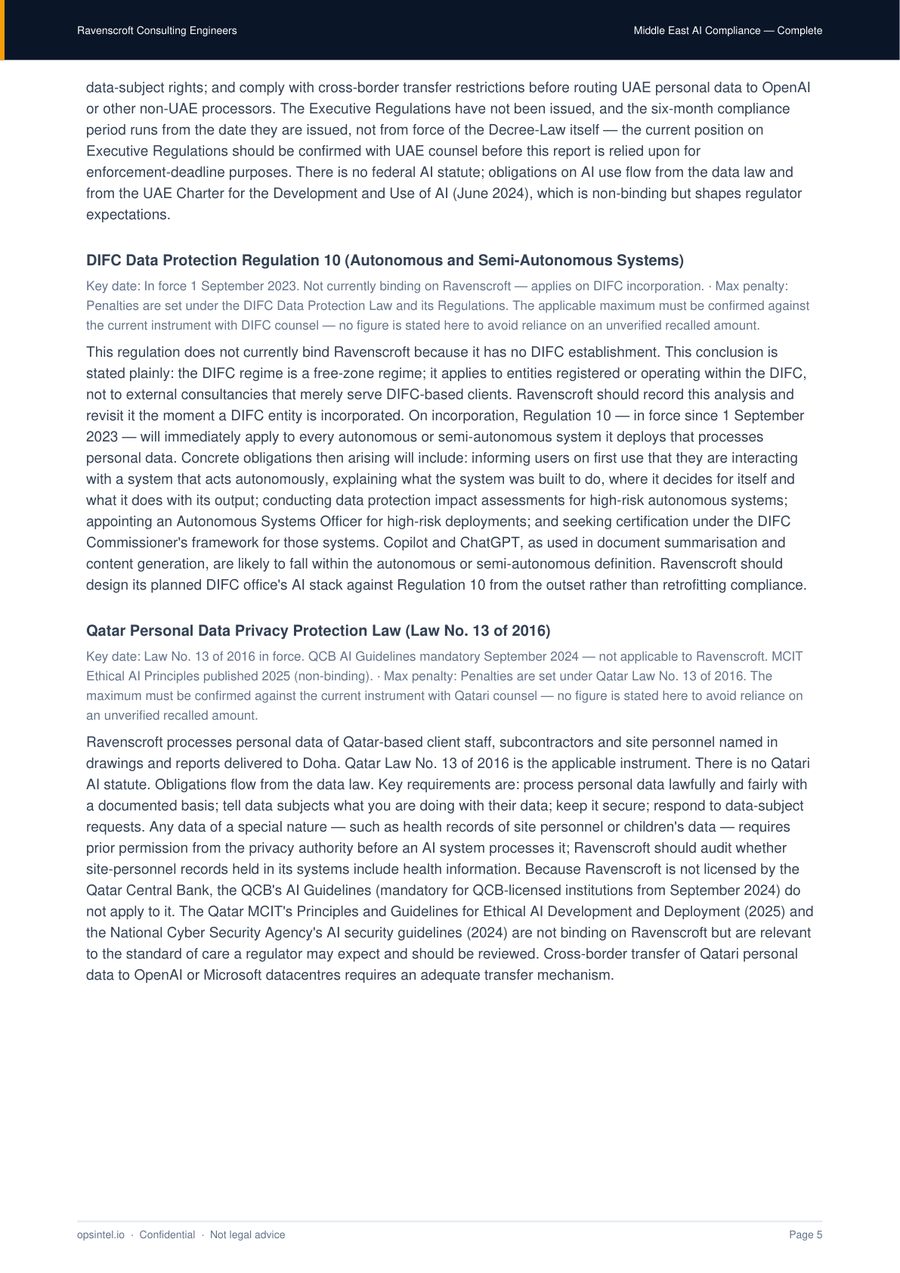
This is not a mock-up or a contents page. It is a genuine Middle East AI Compliance pack — all 11 documents — produced by the same system that will produce yours, for a fictional firm of consulting engineers we invented to test it. They have no office anywhere in the Gulf, and three of the region's regimes reach them anyway. That is the question this pack answers, and it names the regimes that do not reach them as well as the ones that do.
The same work, done in-house.
6 documents to write, and 15 records a year to keep afterwards. Costed against what a member of staff on the median UK salary actually costs an hour:
£1,167+
Your own staff — 45 hours of their time
£797/year
Middle East AI Compliance — in your inbox by the end of the business day
Marked + because the reading is not in that figure yet — we are still counting this market's statutes, so the real in-house cost is higher than shown, never lower.
Find out where you stand in Middle East.
A free call, no pitch deck. We will tell you which of the obligations above reach your business and which do not — including if the answer is none of them.